Built to give you total confidence
Compliance data is sensitive. Coadjute controls who can see what, records what was checked and shared, and keeps an audit trail you can verify.
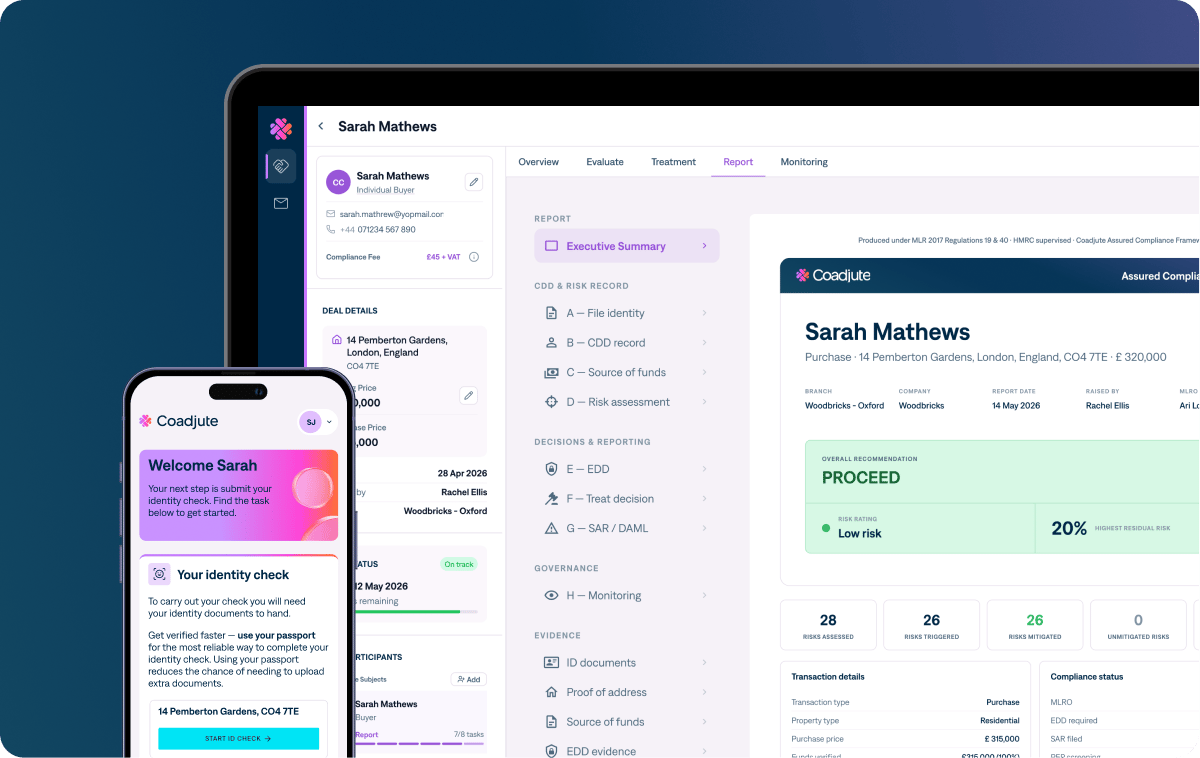
The right access, for the right people
-
Access controls and multi-factor authentication
Controlled access across every organisation taking part in a transaction, with multi-factor sign-in.
-
Role-specific workspaces
Each participant sees the part of the transaction that matters to them, and nothing they don’t need.
-
A verifiable audit record
A confidential ledger provides traceable evidence of the checks recorded and the information shared.
-
Permissioned sharing
Downstream professionals review existing AML evidence only with permission, in a controlled way.
-
Government-certified digital ID
Customers verify their identity through a government-certified digital identity provider, with liveness checks and passport chip reading.
-
Records kept, then deleted
Records are kept for five years after the relationship ends, then personal data is deleted unless an exception applies.
The details your procurement team will want
1
Cyber Essentials
Certified
Independently tested and working towards international standards
Coadjute is Cyber Essentials certified, with ISO 27001 certification targeted for Q2 2027 and SOC 2 Type I assurance planned for 2027.
We also undertake independent penetration testing to assess the security of our systems.
For your IT and procurement teams: We can provide further details of our certifications, security testing and progress towards independent assurance on request.
2
Single sign-on for groups
Sign-on
SAML and OIDC single sign-on is available for group accounts, so your identity provider controls who can sign in and joiners and leavers are handled once. Multi-factor authentication applies to every account without SSO.
3
Tested recovery, published status
Continuity
Business continuity and disaster recovery plans are tested every year, with a recovery time objective of 4 hours and a recovery point objective of 1 hour. Platform availability and incidents are shown on a public status page, status.coadjute.com, which you can subscribe to.
4
Within 24 hours
Breach notification
If a personal-data breach affects your data, we notify you within 24 hours of becoming aware of it, with what is known, what is affected and what we are doing, so you can meet your own 72-hour obligation to the ICO.
5
Hosted in the UK
Hosting
Customer and case data is hosted in the UK, on Microsoft Azure (UK South, with UK West for backup), with access controlled by role and multi-factor sign-in. Customer records are stored only in the UK; Clara prompts and email/SMS messages are processed transiently in the UK/EU region and are not stored there. See where each sub-processor processes data →
6
You’re the controller. We’re the processor.
Data protection
Your agency is the data controller and Coadjute the processor for your customers’ CDD records, under a standard data processing agreement. Coadjute is controller for two things only: the customer’s own payment and consumer-contract record for the check, and the aggregated, anonymised service MI (volumes, attainment, refer rates) in which no customer or case is identifiable. The sub-processors are listed below by category and region. Changes to the list are notified to you in advance.
7
Tested every year
Testing
An independent penetration test every year, on top of multi-factor authentication, role-specific workspaces and the audit ledger.
8
Liability protection and professional insurance
Insurance
Coadjute has clear liability protections and contractual caps in place for every contracting entity, backed by professional indemnity insurance. This provides reassurance that your agency has protection should something go wrong with the services we deliver.
Full details of our liability arrangements and insurance cover are included in your service agreement.
9
Scaling for peak demands
Capacity
Experienced specialists, with the capacity to support your agency
Our UK-based Service Delivery team includes specialists and senior reviewers who plan ahead for busy periods, with additional trained specialists available to maintain service levels as demand grows.
For your IT and procurement teams: All specialists undergo background checks before accessing customer data, with screening repeated every two years. Competence is assessed at recruitment and annually, and we plan recruitment and capacity around customer demand.
10
Referred to you, within one working day
Suspicions
A suspicion is referred to your Nominated Officer within one working day, with the evidence and our reasoning, and a suspicious activity report prepared for their decision. Coadjute staff who form a suspicion refer it to you; they do not report to the NCA on your behalf. The reporting decision is your Nominated Officer’s, and nobody tips off the customer.
11
A service provider, not your supervisor
Regulatory position
Coadjute is a service provider, not an HMRC-supervised relevant person. Responsibility for compliance stays with your firm, which is why everything we do is visible to you and can be examined.
12
Managing customer data
Data storage and processing
All customer records are securely stored in the UK using Microsoft Azure. We use trusted, specialist providers for identity verification, screening, AI assistance and communications. Any temporary processing outside the UK takes place within the UK/EU region, with appropriate data protection safeguards. All providers are documented in our Data Processing Agreement (DPA).
We only share the information needed for each service, such as identity checks, screening or sending reminders. Clara's AI provider processes information temporarily and does not retain customer data or use it to train AI models. All sub-processors are disclosed in our DPA, with changes notified 30 days in advance.
Now you know it’s possible
Come and see your Coadjute service in action
Book a free 30-minute demo to discover how Coadjute works and how we can help your agency.